Skip to product information
1 of 3

Exploit Pack

Exploit Pack

Exploit Pack

Regular price €1.200
Regular price €1.200 Sale price €1.200
Sale Sold out

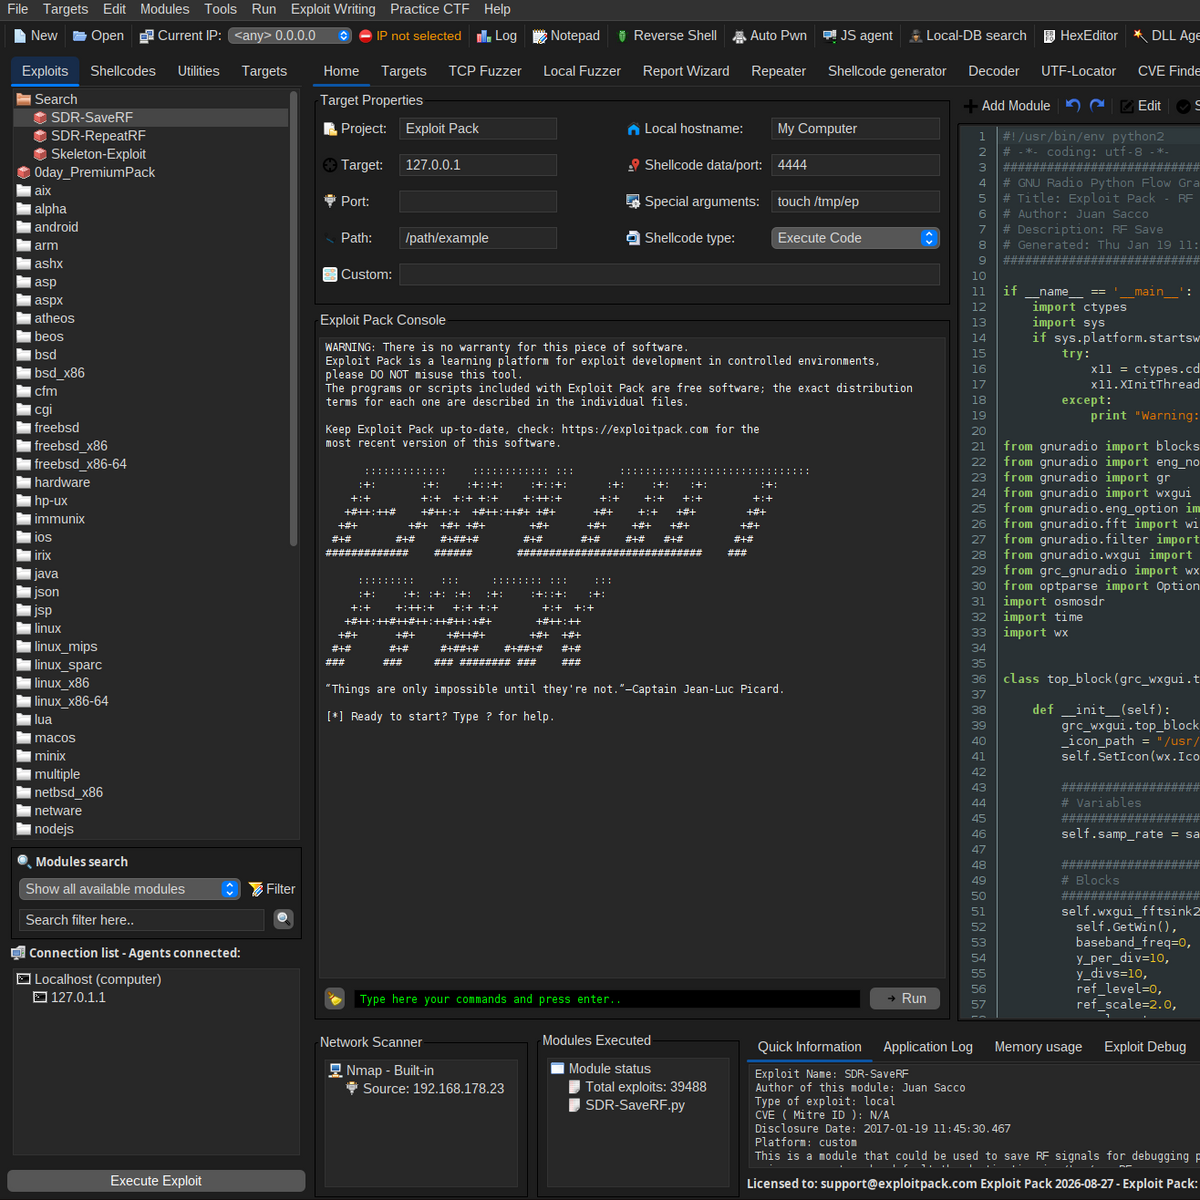
Exploit Pack exploitation framework for Exploit Developers and Penetration Testers. Develop, edit, validate exploits, and gain initial access. Exploit Pack includes a robust set of tools for payload generation, post-exploitation, evasion, and automation. 

Standalone Edition
This license provides the established standalone edition of this product. It does not include the enhanced EP3 edition or EP3-exclusive research, integrations, automation, and operational capabilities available only through Ultimate Pack.

Do you need a quote? Contact us

View full details

The Initial Access Framework

Exploit Pack is a professional exploitation framework with a library of more than 39,000 exploit modules and techniques from our lab, developed by a team of exploit developers and penetration testers.

It includes a set of tools for payload generation and automation, focused on gaining and validating initial access.

With a 1-year Exploit Pack Framework license, you get full access to all features of the tool, plus updates and technical support for you and your team.

Do you need a quote? Contact us

  • Exploit database and research

    Exploit Pack provides access to an internal exploit database containing more than 39,000 exploits, plus continuous updates with techniques from our own research. These exploits are categorised to support exploitation during security assessments, offering broad coverage across platforms, services, and vulnerability types for testing and validation.

  • CVE lookup and reporting

    Exploit Pack includes helpers for referencing known CVEs during exploitation work, allowing users to correlate exploit modules with public vulnerability identifiers. In addition, a built-in HTML penetration testing report generator enables structured documentation of exploitation results, supporting clear communication of findings and impact in assessment reports.

  • Sidekick Feature

    Deploys a helper application (Sidekick) on Windows. When connected to the Sidekick app, the exploit is run on the target system, and the output is received directly in Exploit Pack. The exploit can then be debugged remotely using Ghidra or WinDBG with the Sidekick plugin. Instead of manually transferring files, running payloads, and collecting output, Sidekick acts as a bridge between the development environment and Exploit Pack.

  • Exploit Editor

    A built-in exploit editor designed to support the creation, modification, and testing of exploit code within the framework. The editor provides a structured environment with syntax highlighting and direct integration with the module system, allowing users to edit exploits, manage metadata, and execute modules without leaving the platform. This integration helps streamline exploit development and iterative testing.

  • AutoPwn and Network Scanning

    The framework provides integrated network scanning capabilities combined with AutoPwn-style workflows. Discovered services can be automatically matched against available exploit modules, enabling rapid transition from service identification to exploitation attempts. These workflows are designed to streamline repetitive tasks while still allowing manual control and validation at each stage.

  • Fuzzing tools

    Exploit Pack includes fuzzing tools for remote TCP services, local file-based targets, and socket-based communication. Supporting utilities such as pattern and offset generators help identify crash offsets during exploit development, while UTF locator tools assist in locating payloads within memory. Together, these features support both vulnerability discovery and exploit reliability testing.

Latest changelog version 19.05:

  • Loading times are now faster
  • Dark mode is now available. Help -> Dark-mode
  • New feature: Sidekick. Deploy a Sidekick app on Windows to assist you during your Exploit Development process
  • When connected to the Sidekick app, an exploit can be run directly on the target from the editor, and the output returned to EP
  • An exploit can be debugged remotely with Ghidra using the sidekick plugin. 
  • General improvements in the GUI and menus
  • Bug-fix: When selecting Utilities, the tab was incorrectly set
  • Bug-fix: Selecting an exploit, XML without a code file throws an error
  • Bug-fix: Exporting the exploits folder to a zip file crashes in certain conditions: file not found, name error.
  • Bug-fix: Importing exploits from a .zip file crashes in certain conditions:  file not found, name error

Exploit Pack Licensing FAQ

What type of license is included?

All our tools are provided under an annual license.

Do licenses renew automatically?

Licenses are not automatically renewed. You may choose to renew each year at your own convenience. Special pricing applies to renewals.

How many users can use one license?

Each license is issued on a single-user basis. Sharing between multiple individuals is not permitted.

Integration with other tools

After you gain initial access with Exploit Pack, the workflow continues seamlessly: deploy a Control Pack agent to consolidate access, collect information, and integrate findings into your reporting flow. Designed to hand off cleanly to post-exploitation tooling.

Can I use the license against multiple targets?

Yes. While some tools in the industry restrict you to a limited number of targets, our licenses allow you to use the tool against as many machines as needed.

Delivery of licenses

Licenses are delivered digitally to the email used at purchase. Since they are sent manually, delivery may take up to 24 hours (usually faster).

Once the order is confirmed and the license has been delivered, it cannot be transferred, and refunds will not be issued.